Entertainment
January 1, EXPOSED: Hackers Use Google Ads to Hide Dangerous AI Downloads

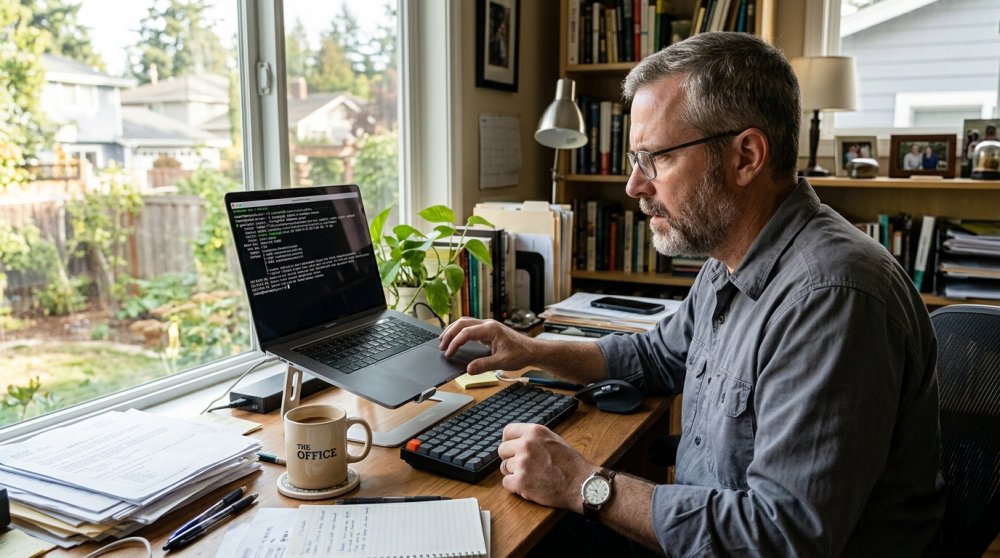
Wyatt’s Take
- Google ads are pushing fake AI downloads that trick folks into running harmful commands on their Macs
- Scammers are hiding behind trusted names like Bing and Claude to make their schemes look safe
- Simple steps like going straight to official sites can keep your computer and your information secure
You type Claude into Google looking for the popular AI tool and spot a sponsored result. The link shows bing.com as the destination, which might seem safe since Bing belongs to Microsoft.
Clicking that ad sends you through several redirects before landing on a fake Claude download page. Security researchers at Push Security found this scheme they call Adception.
The attack starts with a Google search for Claude Mac. The sponsored result displays bing.com as its destination. That address might seem reassuring because Bing belongs to Microsoft. However, clicking the advertisement sends users through a series of redirects.
First, Google’s advertising system processes the click. Next, Bing’s legitimate click-tracking service forwards the browser to a compromised WordPress website belonging to a South American retailer. Finally, that website sends the visitor to a fake Claude download page.
The final website, claude-desk-code[.]com, imitates the real Claude download experience. It presents what appears to be a legitimate macOS installation option. By the time someone reaches the page, they may have little reason to suspect the journey began with a malicious advertisement.
The scammers added another layer of deception to make their operation harder to detect. The compromised retailer’s website checks whether visitors arrived through Bing and whether their browsers send certain information. Meanwhile, the fake Claude website checks whether visitors came from Google or Bing.
Push Security calls this technique cloaking. Attackers use it to control who reaches their malicious content while showing something harmless to other visitors. In this case, the researchers observed two separate checks designed to protect the attack from unwanted attention.
The result is a carefully constructed path that makes a dangerous destination appear more trustworthy than it really is. The fake Claude page displays an installation command that appears to come directly from Anthropic, the company behind Claude.
According to Push Security, the substituted command uses Base64 encoding to conceal an attacker-controlled website. When someone runs the pasted command in Mac Terminal, it first displays a reassuring message claiming that Claude is being downloaded from its official website.
Behind the scenes, the command decodes the hidden address, downloads a remote script and sends it directly to the Mac’s Z shell for execution. That means the person running the command sees references to Claude’s legitimate website even though the Mac is executing code from an unrelated server.
Push Security identified several additional websites associated with the same malicious toolkit. The researchers found matching installation commands and similar fake installer interfaces across those sites.
Google confirms it has taken action against the advertiser accounts associated with the reported campaign. “We’ve suspended the advertiser accounts running the reported campaign. Using ads to distribute malware is an egregious violation of our policies, and we consistently update our detection systems to stay ahead of bad actors’ evolving tactics,” a Google spokesperson told CyberGuy.
Microsoft also responded to CyberGuy’s request for comment, confirming that its security protections identify the malicious indicators described in the research. A Microsoft spokesperson told CyberGuy, “We take reports of malicious online activity seriously and continuously work to help protect customers from evolving threats. Microsoft Defender protections detect and block the malicious indicators identified in the report.”
Instead of searching for a download and clicking the first sponsored result, go directly to Claude’s official download page. Anthropic provides a macOS download there, so you can install the desktop application without relying on an unfamiliar website.
Be especially careful when a website tells you to copy a command into your Mac’s Terminal. Terminal commands can download software, change system settings and execute scripts. Even legitimate-looking instructions can become dangerous when they come from an untrusted source.
A website’s Copy button can place different text on your clipboard than what appears on the page. Before running an unfamiliar command, paste it into a plain-text editor and compare it with the instructions. Watch for unexplained web addresses, encoded strings or commands that download and immediately execute remote scripts.
Install macOS security updates and keep your browser current. Additionally, use strong antivirus software that offers real-time protection against malicious downloads and suspicious activity.
A sponsored placement means someone paid to promote a link. It does not guarantee that the destination is safe. Before clicking, check the advertiser by selecting the three dots next to a Google search ad. You can review who paid for it and check the advertiser’s verification status.
Always confirm you’re visiting the software developer’s official website before downloading anything. If an ad looks suspicious, use its three-dot menu to select “Report this ad.”
What concerns me most about this attack is how much effort the scammers put into making everything look familiar. You start with Google, pass through a legitimate Microsoft service and eventually arrive at a page that looks like it belongs to a popular AI company.
Then, with one click of a Copy button, the website quietly substitutes a command that could put your Mac at risk. I’ve always encouraged people to pay attention to website addresses before downloading software. That’s still important, but this case shows why checking the address alone may not be enough.
The attackers used trusted services to disguise where their link was taking people. My advice is to go straight to the software developer’s official website, especially when installing AI tools. And whenever a download page asks you to run something in Terminal, make sure you understand exactly what you’re authorizing.
Wyatt Matters
Hardworking Americans shouldn’t have to worry about their computers getting hijacked just because they want to try new technology. When companies like Google and Microsoft let ads push people toward scams, it shows how far we’ve drifted from honest dealings and common sense protection for everyday folks.

-
 Entertainment3 years ago
Whoopi Goldberg’s “Wildly Inappropriate” Commentary Forces “The View” into Unscheduled Commercial Break
-
 Entertainment3 years ago
‘He’s A Pr*ck And F*cking Hates Republicans’: Megyn Kelly Goes Off on Don Lemon
-
 Featured3 years ago
US Advises Citizens to Leave This Country ASAP
-
 Featured3 years ago
Benghazi Hero: Hillary Clinton is “One of the Most Disgusting Humans on Earth”
-
 Latest News3 years ago
Nude Woman Wields Spiked Club in Daylight Venice Beach Brawl
-
 Featured3 years ago
Fox News Calls Security on Donald Trump Jr. at GOP Debate [Video]
-
 Entertainment3 years ago
Comedy Mourns Legend Richard Lewis: A Heartfelt Farewell
-
 Latest News3 years ago
Supreme Court Gift: Trump’s Trial Delayed, Election Interference Allegations Linger